

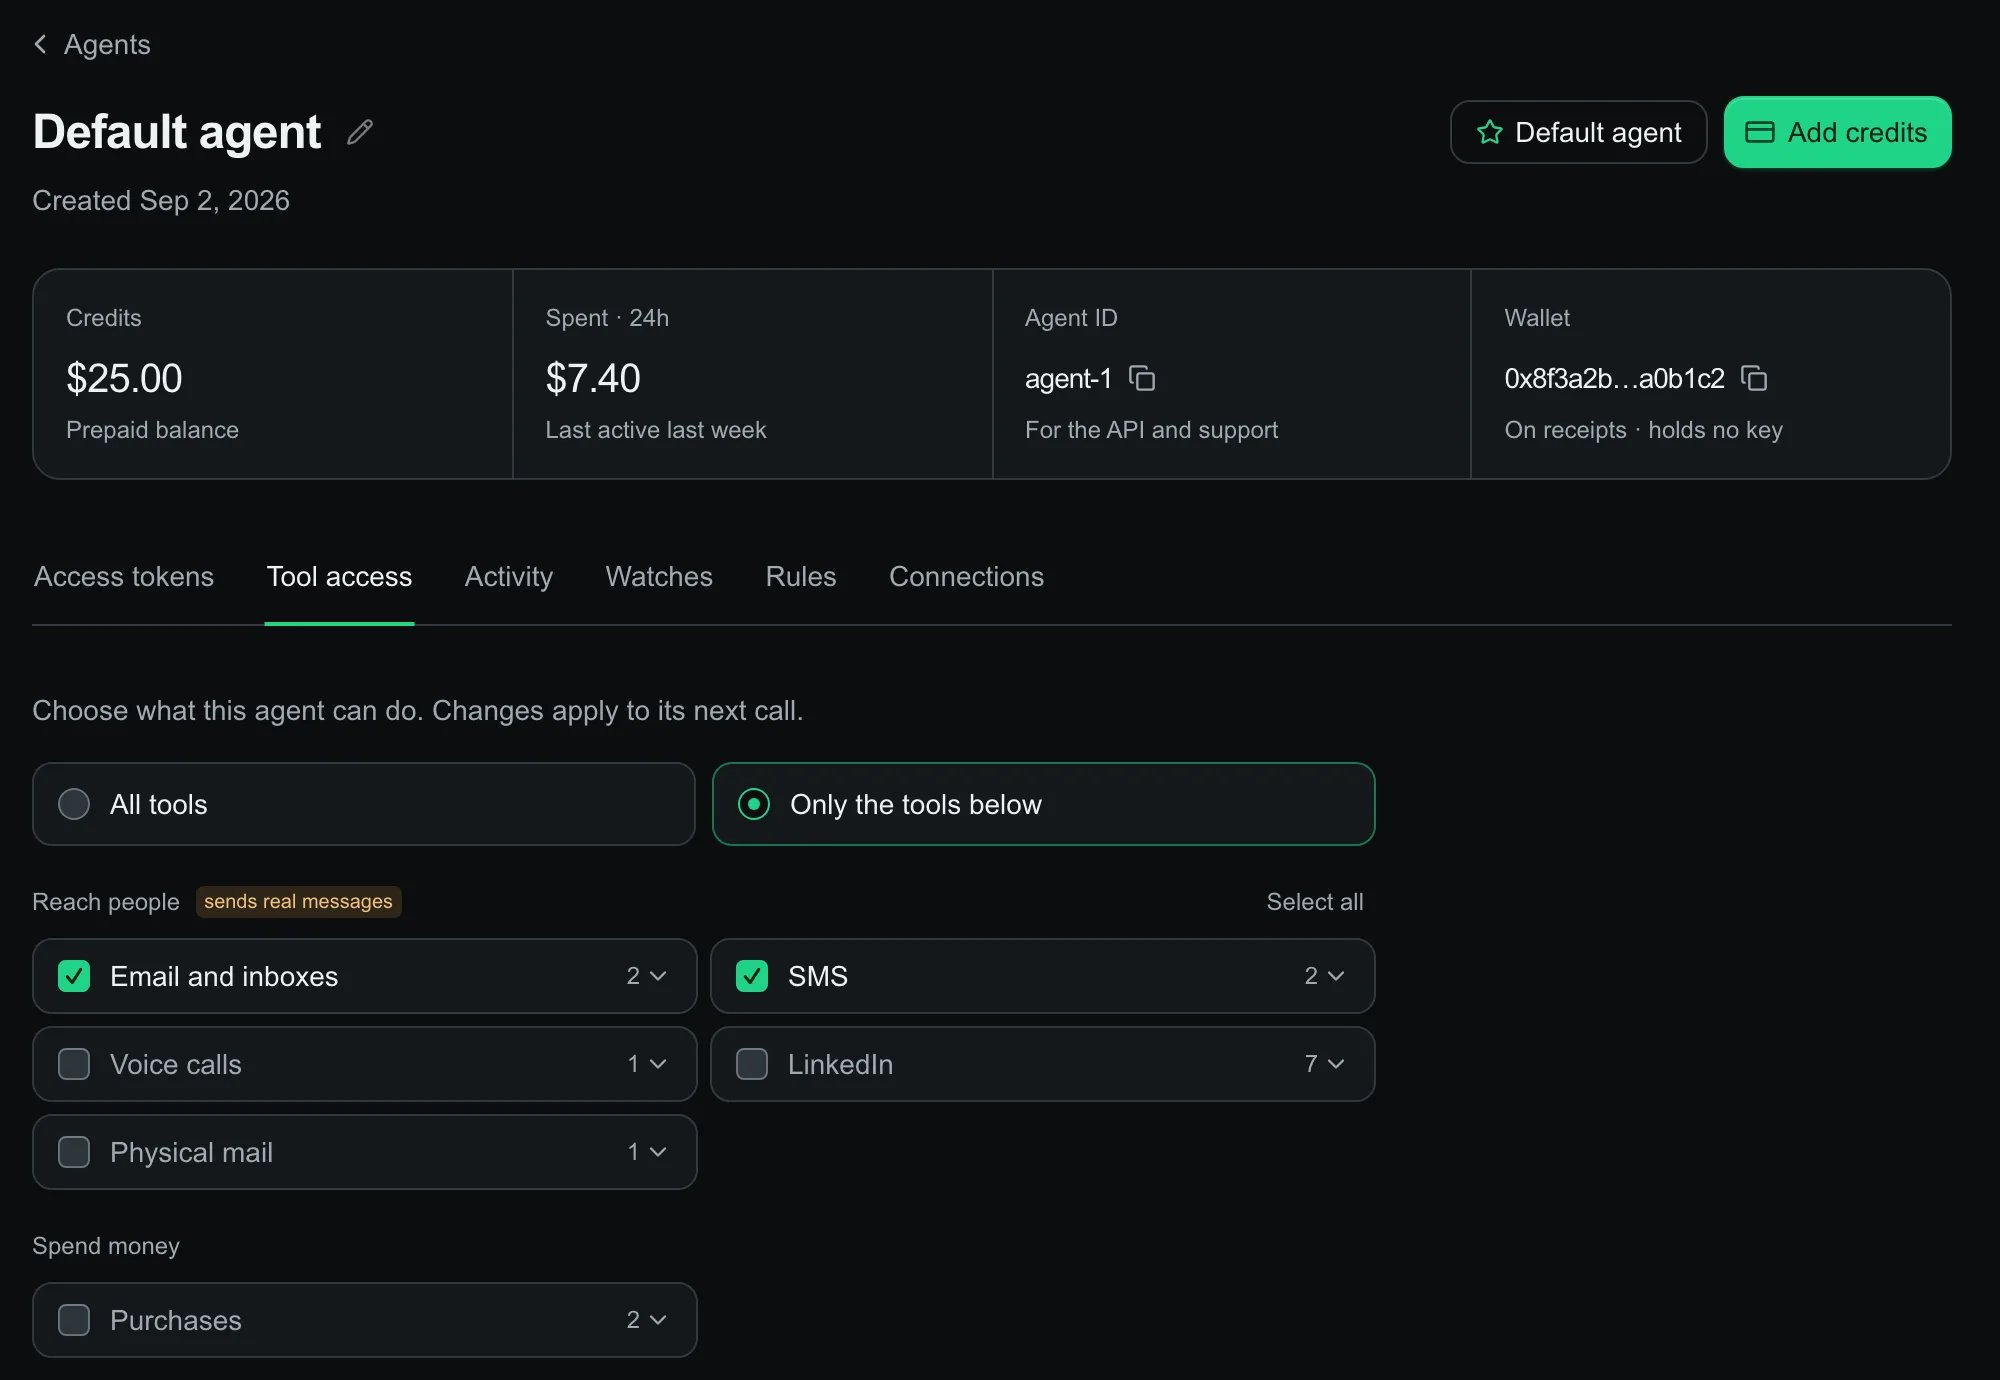
An agent's page: credits, access tokens and the tools it may use.
Access policy
SSO and sign-in
Audit log
Billing and statements
Support
Members
A signup gets a personal workspace, an agent and starter credit. Invited users join their team instead. Invite by email and set roles on Members. Memberships, invitations and role changes are audited.
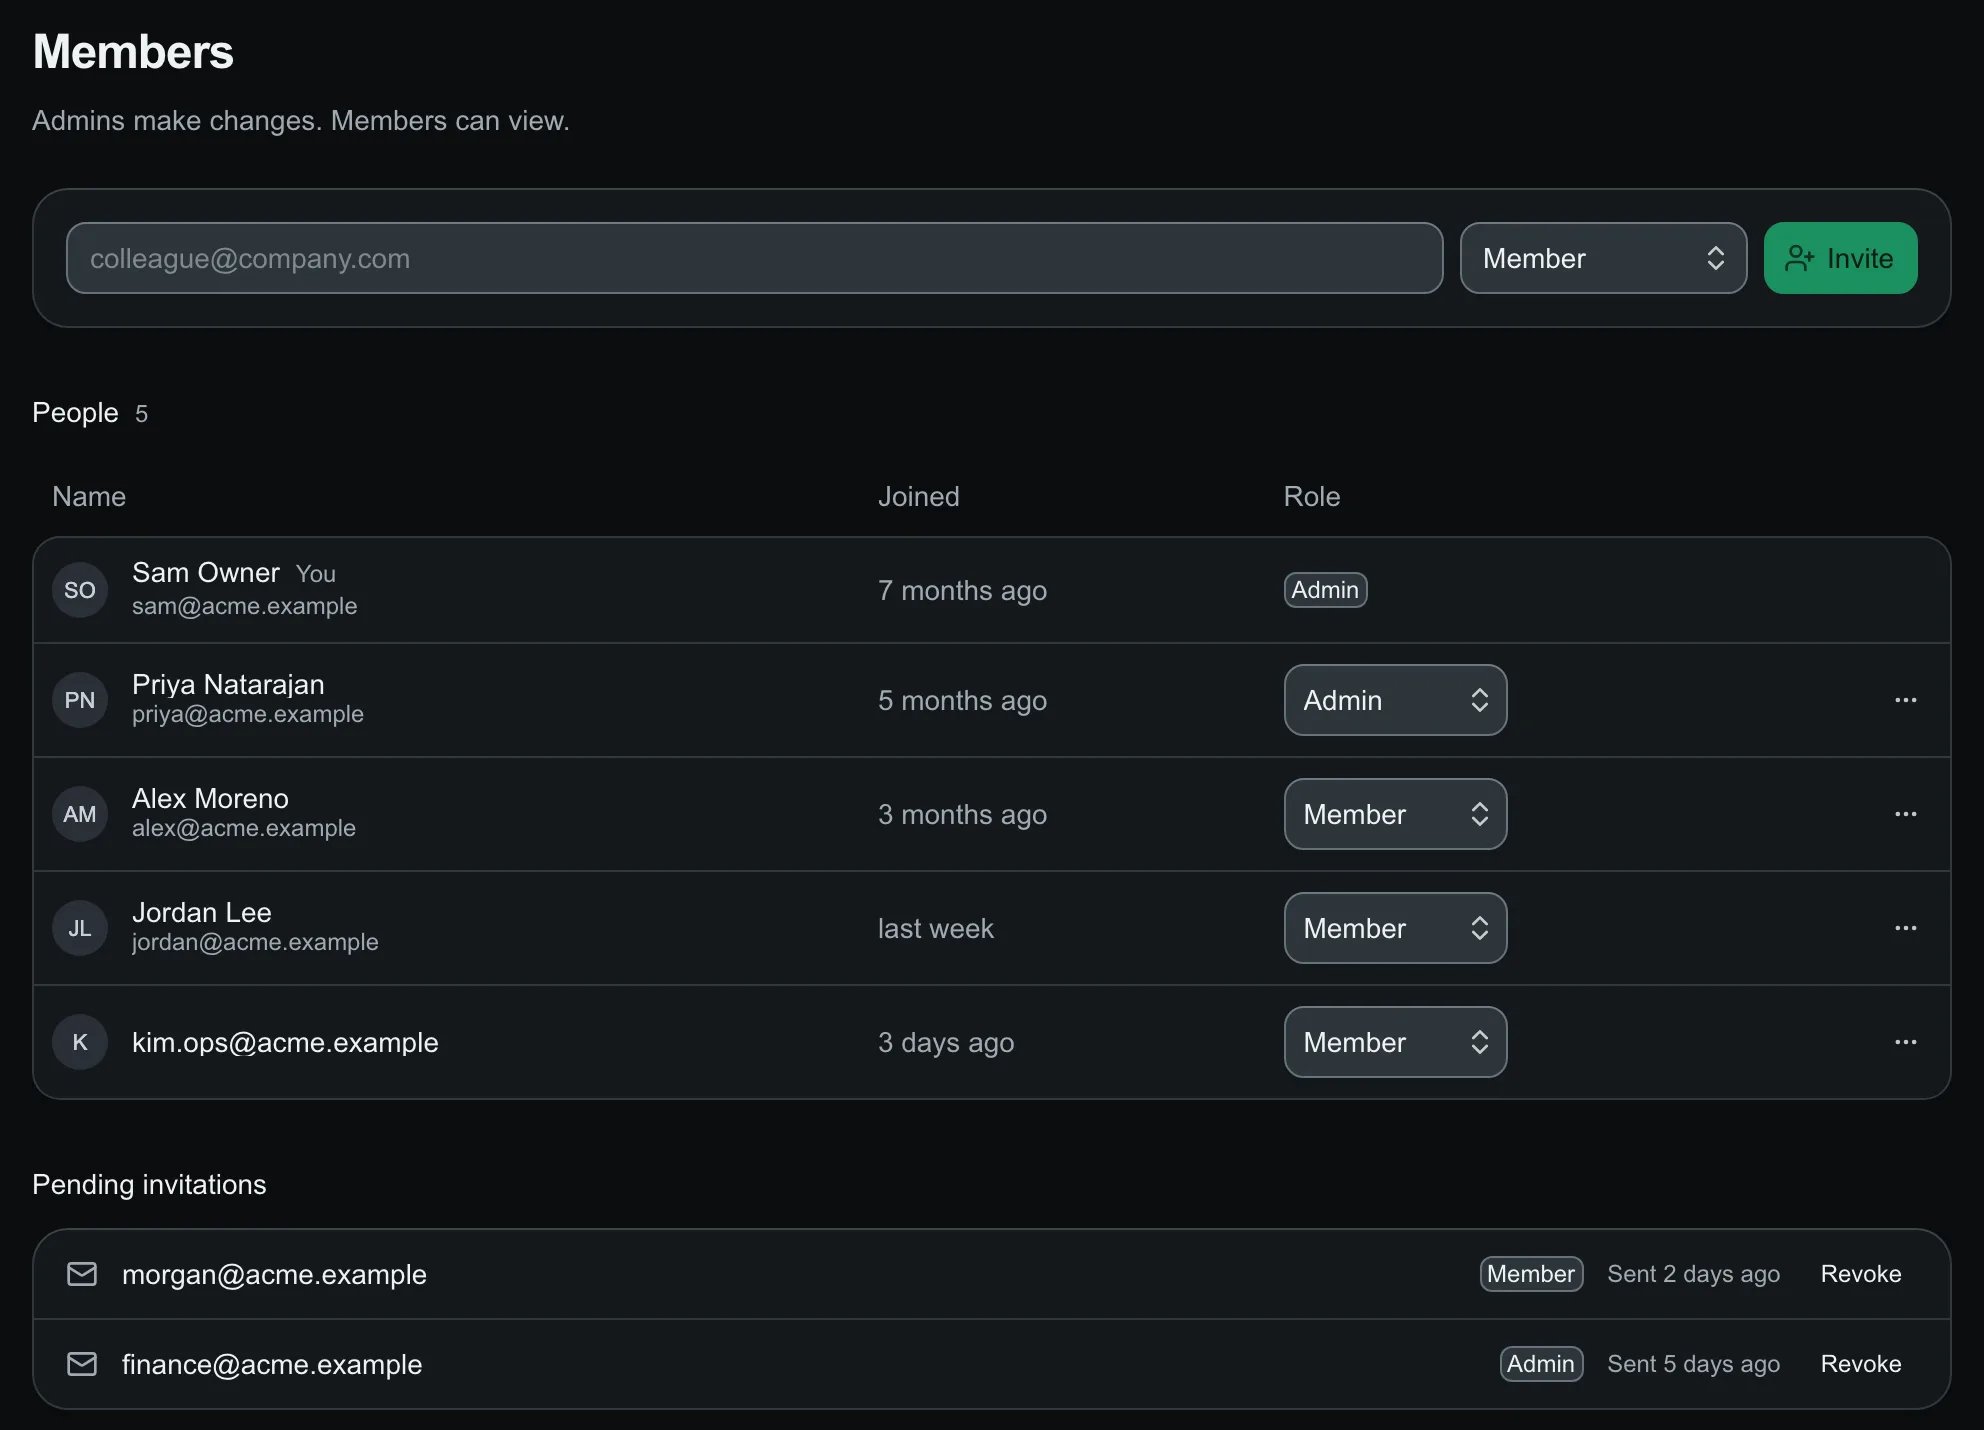
Members: invite by email and set each person's role.
Create an agent
1
New agent
Agents → New agent → name → Create agent.
2
Copy the token
It appears once; OneShot keeps no copy.
3
Use it
Choose an agent’s tools
Every category is open until an admin narrows it in Tool access → Only the tools below. Changes apply next call.
Compute tools also need their categories.
data: lookup, find, resolve, Changes, Benchmark, Watch. Own balance and notifications: always allowed. A token (Access tokens → New token) can narrow categories but never exceed the agent’s grants. A denied call returns 403, error: "tool_not_granted" and the category; no charge.
Revoke access
- Token: Revoke refuses requests and unstarted work; compute goals pause. Running jobs finish. Refused work is refunded like a job that fails before starting.
- Person: remove in Members. Their sessions end within about a minute, unless another organization has them. Agent tokens stay; revoke them. Sign out everywhere ends a member’s sessions.
- Organization: delete in settings; tokens revoked, queued work refused.
- Tool: remove its category; queued work refused.
Credits and spending
1
Add credits
Add credits → amount → card checkout.
2
Wait for settlement
Credits arrive after settlement, usually within seconds; receipt and invoice arrive by email.
Not supported: wallet agents, shared credits, organization approvers.
API
Member sessions only; agent tokens refused: this holds for every/v1/org route. Missing agents and agents outside your organization return 404.
Tool categories return
id, label, description, group and tools (name, title, price, charged: per_call, per_change or varies).
Receipt exports run oldest first by creation time, then id. since and until are ISO 8601 and inclusive, including the entire ending millisecond; limit 1–500, default 100. Pass next_cursor as cursor while has_more; CSV sends X-Next-Cursor (null if absent) and X-Has-More. JSON: { success, data: { receipts, count, has_more, next_cursor } }. CSV: the /v1/audit/receipts columns in order, then access_token_id, compact JSON metadata, cells as in the audit log. Each page is audited with the admin, filters and row count.